The choices you make in your first AWS account are hard to undo later. We work through them with you up front.
You’re moving to AWS or you’ve outgrown your first setup, and the catalog of services is overwhelming. Picking the right ones is half the battle.
We design an architecture that matches your workload, team and budget. Then we set up your accounts, your networking and IAM, the AWS system that controls who can do what. The result is an environment your team can run for the long term.
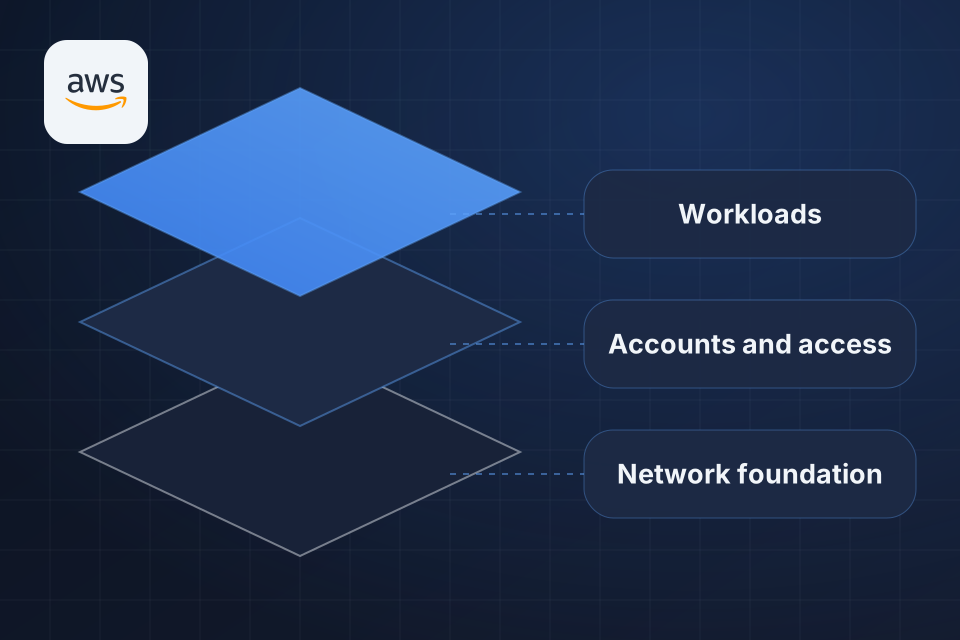
A multi-account strategy using AWS Organizations
IAM and access control design
VPC and network architecture, your private network inside AWS
A landing zone built as your starting foundation
We start with your actual workloads and goals, then match them to the simplest services that fit.
Workloads get split across accounts with AWS Organizations for cleaner isolation, better security and easier billing.
We design IAM roles and permissions so people and systems have the access they need.
Your VPC network and landing zone go in, with governance and security baselines from the start.
We run real AWS production workloads across compute, data and serverless, and we know where the platform’s traps live. Those lessons shape the foundation we build for you, with governance in place from the first account.
Start with your actual workloads and goals, then match them to the simplest services that fit. Most businesses only need a small part of the catalog.
Yes, for any business beyond the smallest. Multiple accounts under AWS Organizations give you cleaner isolation, better security and easier billing.
Yes. We handle migrations from Azure, GCP or on-premises systems to AWS, including the assessment, architecture design and workload migration.
It’s a pre-designed foundation for AWS accounts, with governance, security and networking baselines already in place. It saves a lot of setup work and avoids common mistakes.
Tell us about your project and we'll get back to you within 24 hours.